Know What's Exposed on Your Website
Run a fast, non-destructive security assessment of your website's configuration, headers, TLS, DNS, and common exposure points.
Authorization required. Only scan websites that you own or have explicit authorization to test.
8
scanner engines per run
< 60s
from URL to scored report
100%
non-destructive checks
What we check
Eight modular scanner engines run against your site and return standardised findings with evidence and remediation.
Security headers
CSP, HSTS, X-Frame-Options, Referrer-Policy, Permissions-Policy and cross-origin isolation headers, each with the recommended value.
SSL / TLS
Certificate validity, expiry, issuer, hostname coverage and HTTPS availability, plus HTTP-to-HTTPS redirect behaviour.
DNS security
A, AAAA, CNAME, MX, NS and TXT records, with SPF, DMARC and DKIM checks that separate recommendations from real weaknesses.
WordPress security
Version disclosure, REST API and XML-RPC exposure, readme files, debug logs and publicly detectable plugins and themes.
Exposure detection
Common accidental exposures such as .git metadata, environment files, backups, directory listings, source maps and verbose errors.
Cookie hygiene
Secure, HttpOnly and SameSite attributes on every cookie the site issues on a public page load.
Scan reports
Standardised findings with evidence, risk and remediation, plus a downloadable PDF report for stakeholders.
Scan history
Every scan is stored so you can compare two runs and see exactly what was fixed, what is new and what is unchanged.
How it works
- 1
Enter your URL and confirm authorization
You confirm you own the site or have written permission to test it. The confirmation is stored with the scan record.
- 2
Eight safe engines inspect your site
Ordinary GET/HEAD requests and public DNS lookups only — no exploitation, no logins, no changes to your site.
- 3
Get a scored, prioritised report
A transparent 0–100 score with per-category deductions, evidence for every finding, and clear remediation steps.
Reports your whole team can act on
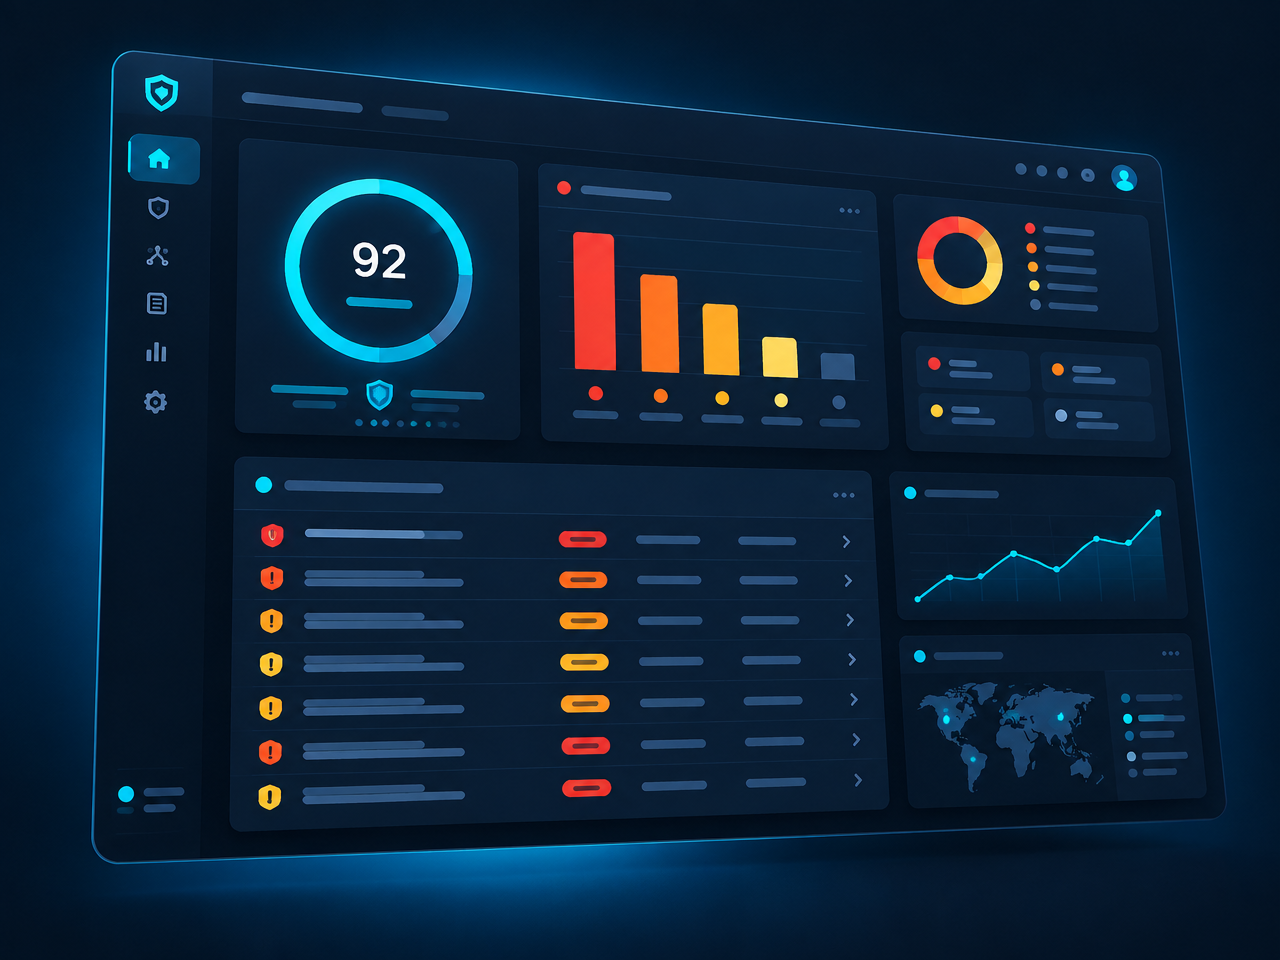
Every scan produces a clear score, severity breakdown and evidence-backed findings. Download a PDF for stakeholders, and compare any two scans to see exactly what was fixed, what is new and what is unchanged.
- Transparent 0–100 score with per-category deductions
- Evidence and remediation for every finding
- PDF export and scan-to-scan comparison
Frequently asked questions
Start your first assessment
Create an account, confirm authorization, and get a scored report in under a minute.
Create free account